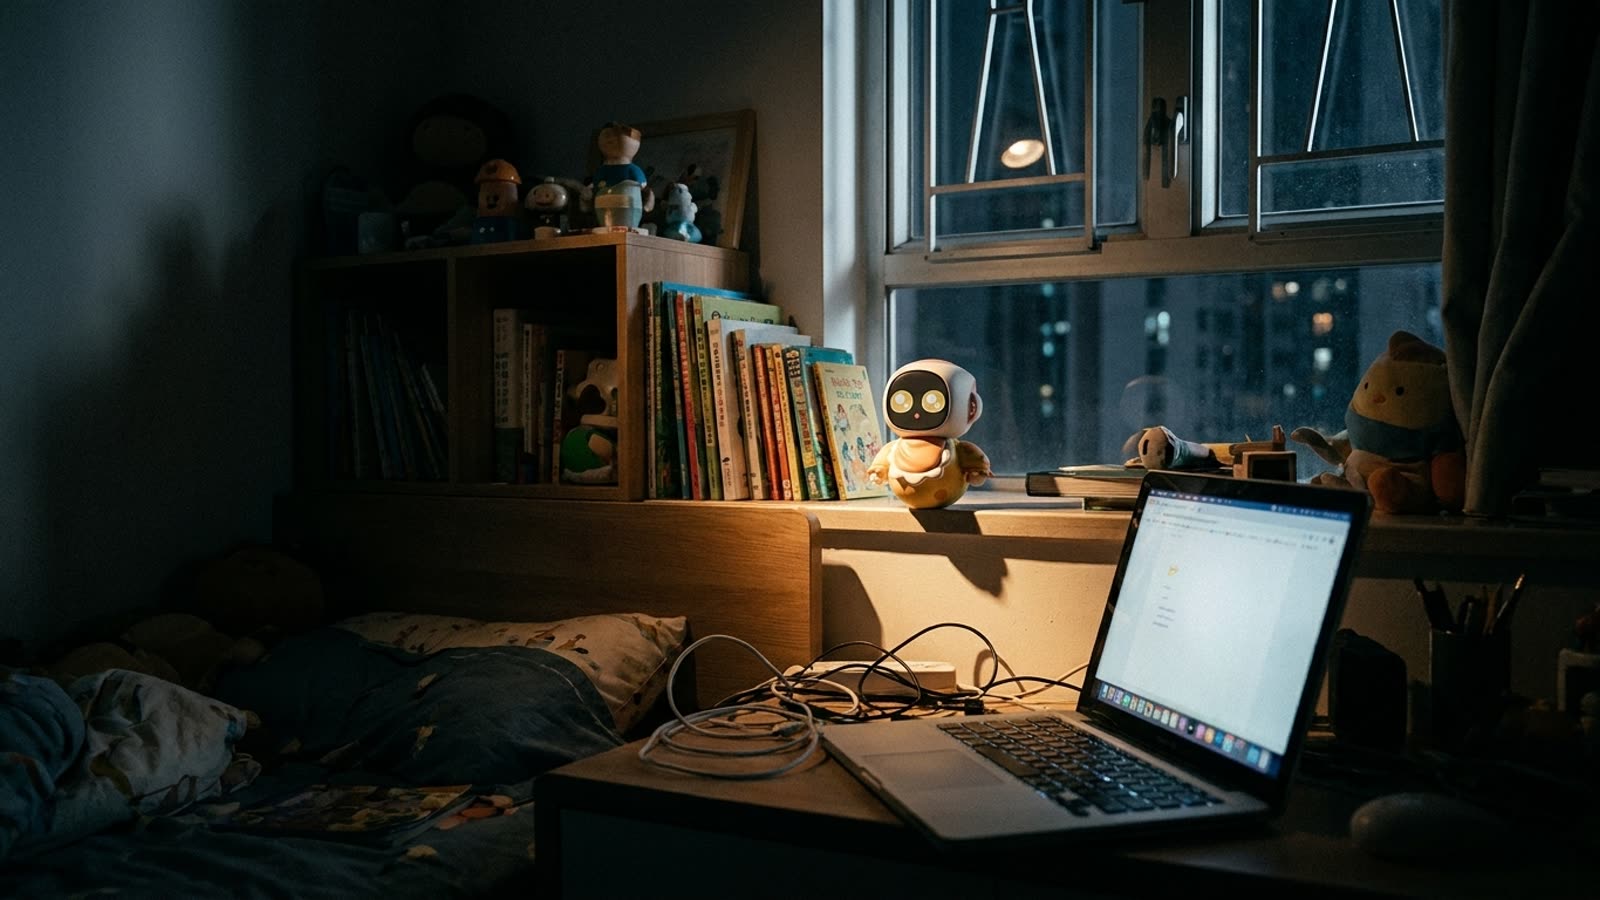
The Eiliko looks like something Pixar might have designed for a toddler: a squishy marshmallow body, cartoon eyes that shift to mirror the user's mood, and a chirpy AI voice ready to chat about dinosaurs or bedtime stories. It is also, according to new reporting from The Verge, a remarkably efficient conduit for shipping intimate family conversations to servers in mainland China—servers that researchers say are trivially hackable.
This is not a story about one dodgy gadget. It is a story about an entire product category—AI-powered companion toys—that has exploded in the post-ChatGPT era without anything resembling adequate regulatory scrutiny or industry self-discipline. Parents who would never hand their child an unlocked smartphone are cheerfully placing always-listening robots in bedrooms, trusting that someone, somewhere, has checked the security posture. In most cases, no one has.
The Eiliko problem in detail
When Eiliko connects to a home Wi-Fi network, it establishes a persistent link to cloud infrastructure hosted in China. Voice recordings—children's voices, often—are processed remotely to power the device's conversational AI. Security researchers found the authentication layer protecting that data to be alarmingly thin: default credentials, unencrypted API calls, and no apparent rate-limiting on requests. In practical terms, an attacker with modest skills could intercept or exfiltrate recordings at scale.
More troubling is the jurisdictional question. Under China's 2017 National Intelligence Law, domestic companies can be compelled to assist state security organs with data access. Whether or not Beijing has any interest in what a six-year-old in Ohio thinks about her goldfish is beside the point; the legal architecture makes opt-out impossible for the manufacturer, and therefore for the consumer.
A market without guardrails
Eiliko is far from unique. The AI companion toy segment has grown rapidly since 2024, fueled by parents eager to give children something more interactive than a tablet and by manufacturers eager to monetize generative-AI APIs. Most of these products are designed in Shenzhen, assembled at scale, and sold globally via Amazon and TikTok Shop with minimal customs friction. Regulatory bodies in the US and EU have been slow to classify them: are they toys, subject to safety standards? Consumer electronics? Medical devices if they claim to help with anxiety? The ambiguity has created a vacuum that less scrupulous vendors are happy to fill.
The Children's Online Privacy Protection Act (COPPA) in the US theoretically covers voice data collected from minors, but enforcement is complaint-driven and penalties are modest. The EU's GDPR offers stronger protections, yet cross-border data flows to non-adequate jurisdictions remain difficult to police in practice. Meanwhile, the devices keep shipping.
Our take
The Eiliko debacle is a preview of a much larger reckoning. As AI capabilities become cheap enough to embed in plush toys, the attack surface for data harvesting expands into nurseries and playrooms. Regulators need to stop treating these products as novelty items and start treating them as networked surveillance devices—because that is what they are. Until then, the safest companion for your child remains a stuffed animal that cannot phone home.